 RU
 KZ
 EN
Access control
Policy-based control over which users and devices are allowed to connect to the enterprise network and what they can access.
Discuss a project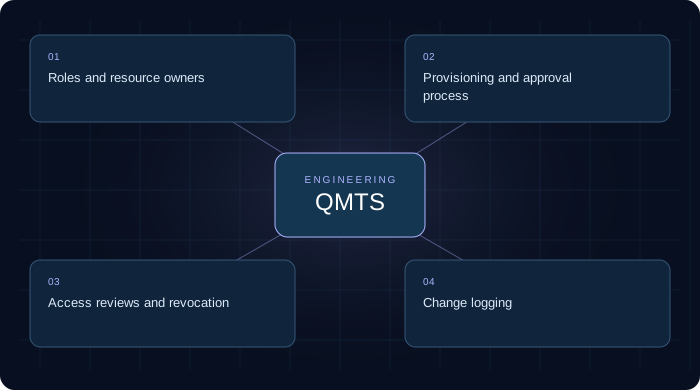
What it is
NAC identifies and authenticates users or devices and applies access policy based on identity, device posture, location or other context.
Why it matters
It helps prevent unmanaged or unauthorized endpoints from receiving unrestricted access to corporate resources.
What shapes the design
- Roles and resource owners
- Provisioning and approval process
- Access reviews and revocation
- Change logging
QMTS delivery scope
We define identity sources and access policy, integrate wired/wireless enforcement, configure onboarding and exception workflows, and test user/device scenarios.
Customer deliverables
A controlled access model with documented policies, authentication flows and operational procedures.
Typical use cases
Enterprise wired and wireless networks, BYOD, contractor access, IoT environments and environments with compliance requirements.
Delivery lifecycle
- 01 Requirements discovery and current-state assessment.
- 02 Architecture, dependencies and implementation planning.
- 03 Technical specification, configuration baseline and delivery preparation.
- 04 Implementation, integration, testing and controlled commissioning.
- 05 As-built documentation, operational handover and managed support where required.
Before we start
To scope a project, describe the goal, users and sites, current systems, timing constraints and desired outcome. Solution scope and service terms are defined after assessment.
Start with your challenge
Tell us what you need to build, connect or improve. An idea, a list of issues or a technical brief is enough to start.
Support coverage and SLA parameters are agreed for each project.
Discuss a project
Leave an email address or phone number so we can respond.