 RU
 KZ
 EN
DDoS protection
Controls and upstream mitigation services designed to keep internet-facing services available during distributed denial-of-service attacks.
Discuss a project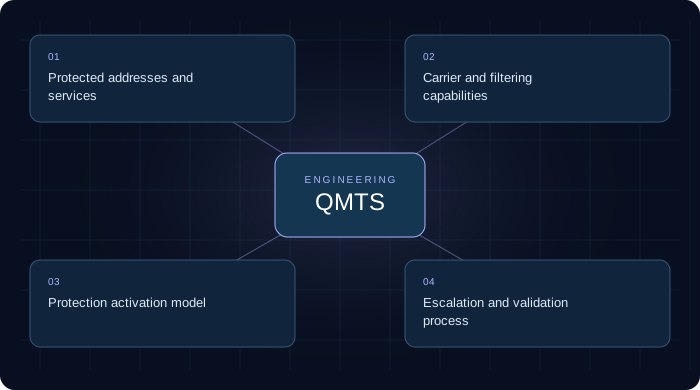
What it is
DDoS attacks attempt to exhaust bandwidth, connection state or application resources by generating malicious traffic from many sources.
Why it matters
Protection is important for organizations whose websites, APIs, VPN gateways or public services must remain reachable during an attack.
What shapes the design
- Protected addresses and services
- Carrier and filtering capabilities
- Protection activation model
- Escalation and validation process
QMTS delivery scope
We assess exposed services and bandwidth, define the protection model with carriers or security providers, establish routing/activation procedures and validate operational escalation.
Customer deliverables
A documented DDoS mitigation model with protected prefixes/services, activation procedures and provider escalation paths.
Typical use cases
Internet-facing applications, public services, e-commerce, financial services, VPN gateways and data-center internet edges.
Delivery lifecycle
- 01 Requirements discovery and current-state assessment.
- 02 Architecture, dependencies and implementation planning.
- 03 Technical specification, configuration baseline and delivery preparation.
- 04 Implementation, integration, testing and controlled commissioning.
- 05 As-built documentation, operational handover and managed support where required.
Before we start
To scope a project, describe the goal, users and sites, current systems, timing constraints and desired outcome. Solution scope and service terms are defined after assessment.
Start with your challenge
Tell us what you need to build, connect or improve. An idea, a list of issues or a technical brief is enough to start.
Support coverage and SLA parameters are agreed for each project.
Discuss a project
Leave an email address or phone number so we can respond.